Flowguard Anti-DDoS · traffic visibility and mitigation for ISPs, with nothing to install
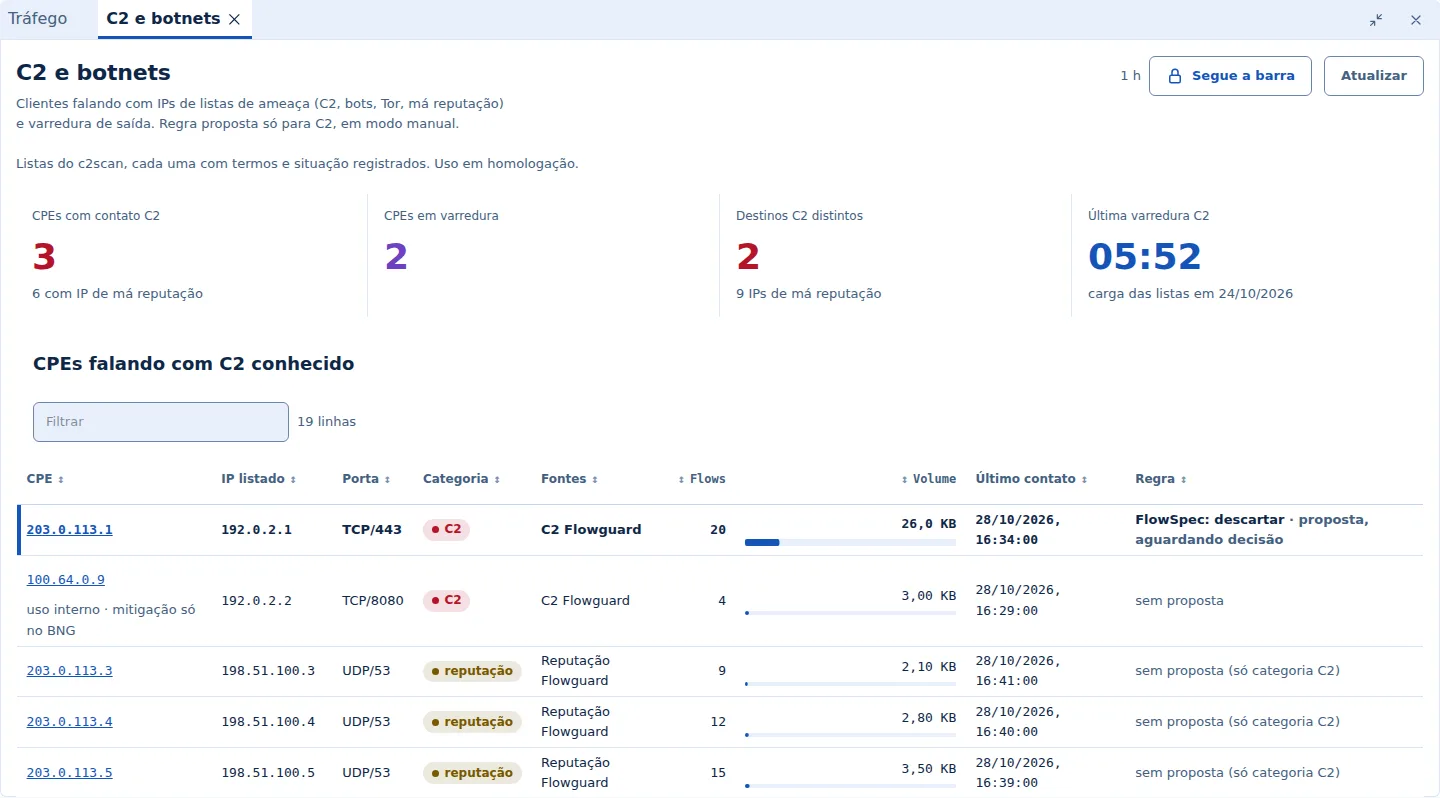
C2C - Find out which subscribers talk to botnets and block them.
Devices on your network that contact known, catalogued C2 servers; apply mitigation with a fixed ACL or BGP FlowSpec.
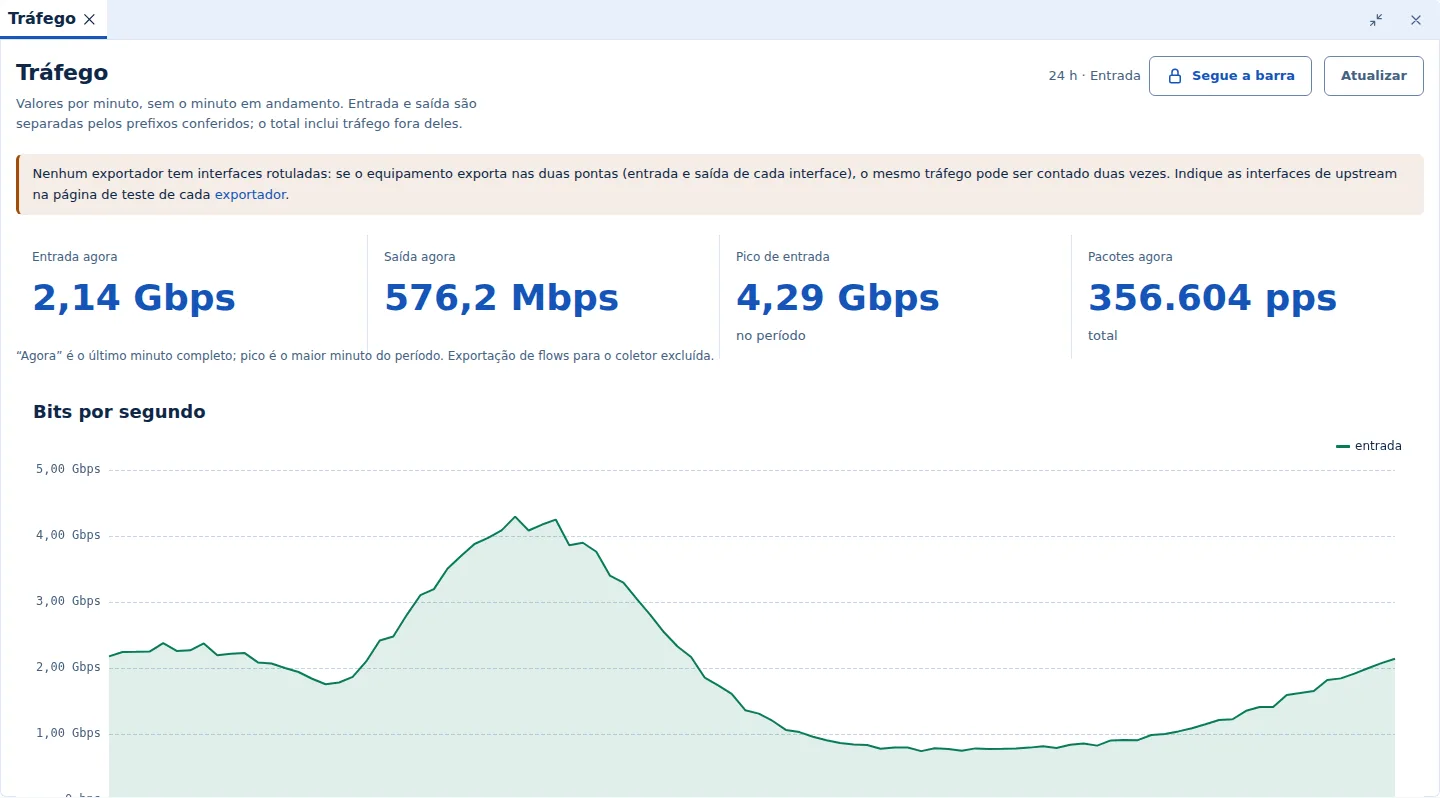
See your network traffic as it happens
Inbound and outbound by prefix, ASN, protocol and port, processed in under 1 s at the median and shown minute by minute.
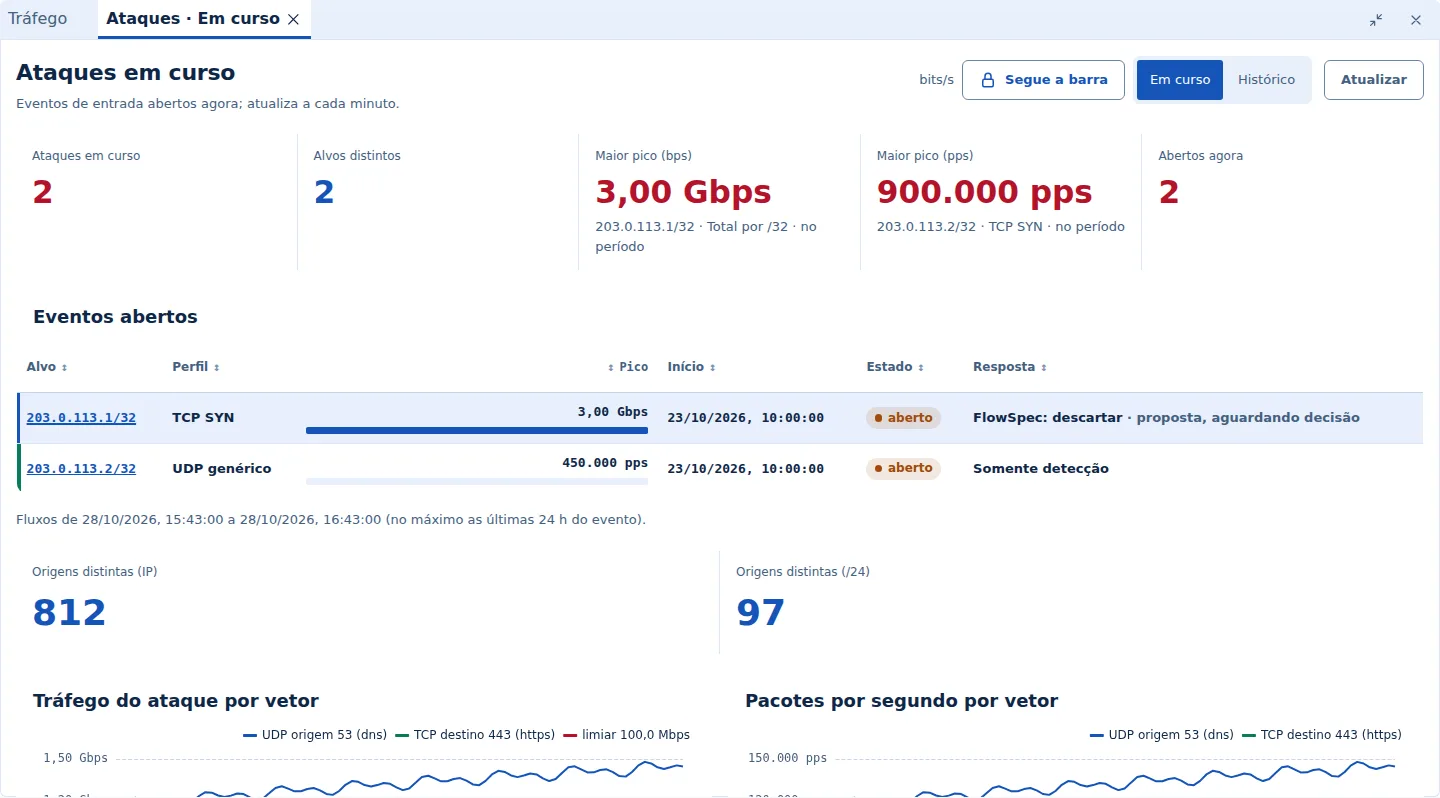
Attacks identified by the threshold you set
Each prefix has its own detection rules. Once the limit is crossed, the event opens with the victim, the vector and the peak, and a mitigation rule is proposed.
Mitigation over the BGP session, with FlowSpec or RTBH
Rules reach your router over the BGP session with AS61620. The router applies the FlowSpec rule as a filter (ACL).
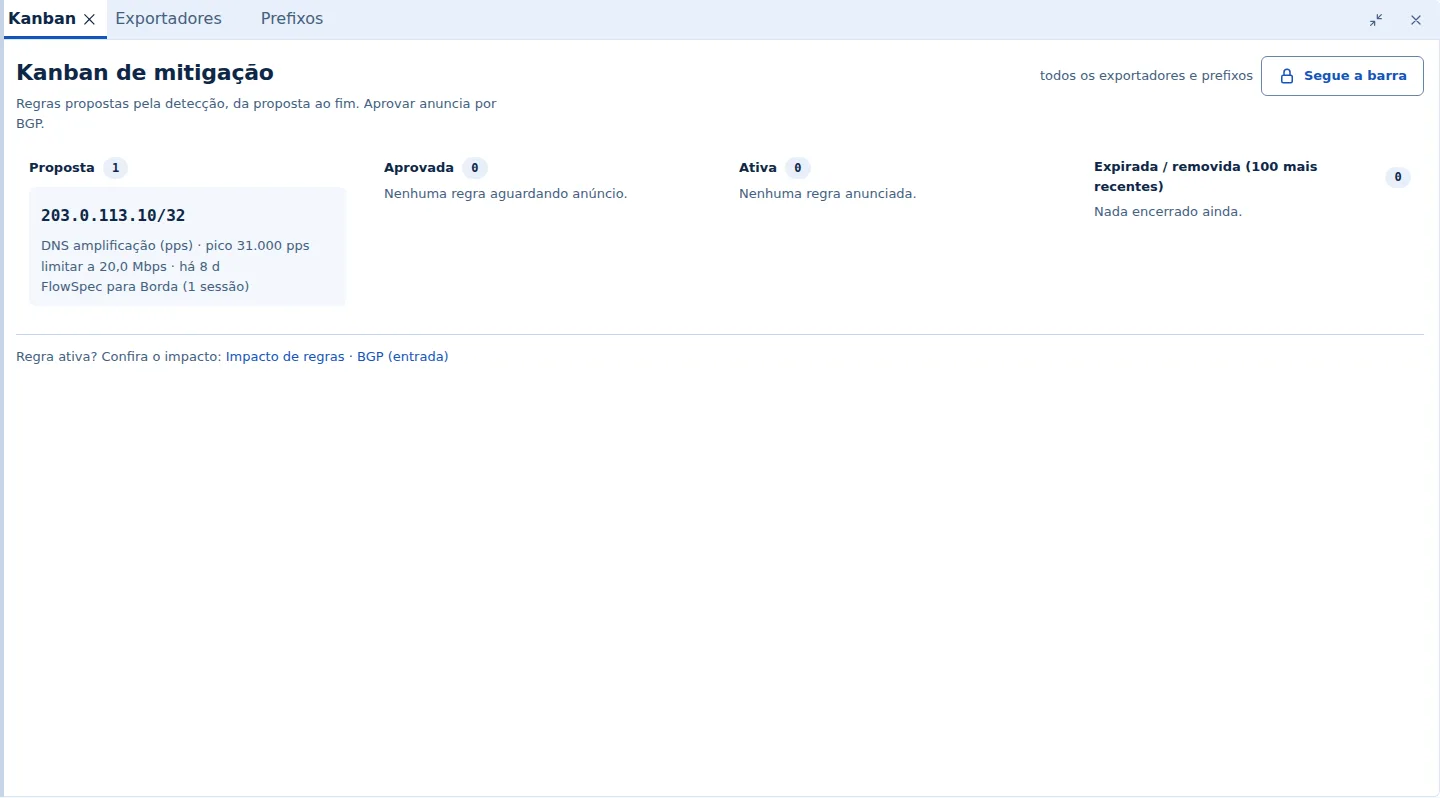
No free trial: the demo uses fictitious data and shows the same screens as the dashboard.
In an ISP's routine
Situations every ISP has been through
Late at night, the link saturated and the network went down
The attack arrives after hours and the first news comes from a customer. By the time the target and vector are found, the network has already been down.
Threshold detection and mitigationComplaints about slowness, and the cause was an infected CPE
A subscriber router became part of a botnet: it generates strange traffic, lands on block lists and support cannot find the reason.
C2 and botnetsThe link is full, but who is using it?
The carrier's chart shows the total. Without the detail by prefix, ASN, protocol and port, the decision to upgrade or to charge is made in the dark.
Real-time visibility
Features
What Flowguard solves
Real-time traffic
Inbound and outbound by prefix in bits and packets per second, with the source ASN resolved from the BGP table, the protocol and the port.
Processed in under 1 s at the median (0.58 s, measured on 10/25/2026); minute-by-minute charts, without the minute in progress.
Attacks detected by the threshold you set
Threshold templates per prefix, with domain, direction, protocol and port. The event opens with victim, vector and peak, and proposes the response.
Mitigation via BGP FlowSpec or RTBH
The approved rule is announced to your router over the BGP session with AS61620, always restricted to verified prefixes.
Your router applies the FlowSpec rule as a filter (ACL).
Subscribers in botnets, identified
CPEs that contact known command and control addresses, with the remote address, the port and the last contact.
Interfaces and upstream via SNMP
Interface state and traffic, CPU and temperature when the vendor exposes them. Mark the upstream to count only what crosses the edge.
Alerts on Telegram and by email
Attack and mitigation notices in your team's Telegram group or email list, chosen in each rule.
How it works
Screens
Inside the dashboard
Short videos and screenshots from the demo. Use the arrows, the indicators or swipe sideways.
Recordings and screenshots from the demo, with fictitious data and documentation addresses.
Plans
You pay for bandwidth, not for the number of routers
The unit is the monitored traffic band, with sensors (flow exporters) included. Monthly or yearly; to get to know the product, we recommend starting with monthly.
P1
Monitored traffic up to 1 Gbps
2 sensors included
R$ 99,87 / month
Yearly: R$ 1.078,60 total for the period (10% discount).
Additional sensor: R$ 39,87 / month. Buy
SubscribeMost recommended
P2
Monitored traffic up to 5 Gbps
5 sensors included
R$ 188,87 / month
Yearly: R$ 2.039,80 total for the period (10% discount).
Additional sensor: R$ 74,87 / month. Buy
SubscribeP3
Monitored traffic up to 10 Gbps
10 sensors included
R$ 388,87 / month
Yearly: R$ 4.199,80 total for the period (10% discount).
Additional sensor: R$ 138,87 / month. Buy
Subscribe
All plans include
- NetFlow v5/v9, IPFIX and sFlow v5
- Per-minute charts and ASN, protocol and port rankings
- Threshold detection and attack events
- Interfaces via SNMP and upstream marking
Above 10 Gbps
Network larger than 10 Gbps: Flowguard runs inside it
- Local sensor: a dedicated instance on your network, instead of cloud collection.
- Not available for purchase on the website: scope and price on request.
- Installation, hardware, maintenance and local license are not included in the plan prices.
Talk to a specialist
Tell us the size of your network and the sales team will reply.
On-premises deployment
Flowguard on your ISP's infrastructure
Besides the cloud service, Flowguard can be deployed on your network. Requirements, responsibilities and price are defined on request. Installation, hardware, maintenance and local license are not included in the plan prices.
Talk to sales: 21 99711-5461 (phone and WhatsApp) or soc@flowspec.net.br.
Our numbers
The platform in operation
- flow records per minute, all customers
- 111,829
- source ASNs resolved from the BGP table
- 86,581
- between the last flow received by the collector and the reading, with the data already queryable
- 0.2 s
- prefixes in the BGP table (IPv4 and IPv6)
- 1,342,070
Read on 11/8/26, 12:55 PM (Brasília time), when the site was published. These are operational platform figures, not the number of customers. Status
Live terminal: each line is a real platform fact, with the time it happened (Brasília), read every 60 s. Addresses outside 100.64.0.0/10 appear as “customer prefix”.
Frequently asked questions
Questions
Is there a free trial?
No. Access is paid, for one month or one year. To get to know the product first, we recommend the monthly plan. Before buying, the demo with fictitious data and the public documentation show the screens and the setup.
What is the difference between monthly and yearly?
Yearly has a 10% discount over twelve monthly payments and is purchased for the total amount of the period.
What happens at the end of the period?
The subscription renews automatically at the end of each period, with a new charge on the same payment method, until you cancel the renewal. The cancellation takes effect at the end of the period already paid, and access continues until that date.
Can I cancel before the end of the period? Is there a refund?
These are different things. Not renewing means choosing not to buy the following period. To cancel before the end of the period, talk to sales. There is no refund for mere withdrawal or lack of use, except where required by applicable law.
How does technical support work?
By email at soc@flowspec.net.br, Monday to Friday, 8 am to 6 pm (Brasília time), no service on Saturdays, Sundays and holidays. Response times: level 1 within 2 hours, level 2 within 4 hours, level 3 within 8 hours. These are response times, not resolution times. There is no 24-hour support and no chat.
What about phone and WhatsApp?
21 99711-5461 (phone and WhatsApp) handles sales contacts, purchase questions and band changes. Technical issues go by email, where the response times apply.
Does mitigation already work?
Yes. The approved rule is announced to your router as FlowSpec or an RTBH route over the BGP session with AS61620, always restricted to verified prefixes. Your router applies the FlowSpec rule as a filter (ACL).
Do Telegram and email alerts already work?
Yes. Register the channels in the dashboard (Settings, Alerts) and choose for each channel when it is notified: event opened, event closed, mitigation rule live and rule withdrawn.
My network exceeds 10 Gbps. What now?
Above 10 Gbps there is no purchase through the website: service is provided with a local sensor, in a dedicated instance on your network, on request through the sales contact.
Start with collection
Create the account, register the first exporter and watch the flows arrive on the test page.